Penetration testing & AI red teaming, run by the operator you hire.
Founder-led, manual offensive testing for startups, MSPs and growing companies — web apps, APIs, networks, cloud, ICS/OT and the LLMs and AI agents you're shipping. Auditor-ready reports, a free retest within 6 months, and continuous PTaaS when you ship weekly.
Every layer an attacker can reach.
From your public perimeter to the AI agent with access to your inbox. Filter by layer or search for what you need tested.
AI & LLM Penetration Testing
Prompt injection, jailbreaks, data leakage and RAG poisoning in chatbots, copilots and AI features.
Learn more AI SPECIALTYAI & LLMAgentic AI & MCP Security Testing
Tool abuse, excessive agency and MCP server flaws in agents that take real actions.
Learn more AI & LLMML Model & Supply Chain Testing
Malicious model files, unsafe deserialization and poisoned dependencies in your ML pipeline.
Learn more ApplicationsWeb Application Penetration Testing
Manual testing beyond the OWASP Top 10: business logic, authorization, SSRF and injection.
Learn more ApplicationsAPI Penetration Testing
REST, GraphQL and mobile-backend APIs tested for broken auth, data exposure and abuse.
Learn more ApplicationsMobile App Penetration Testing
iOS and Android apps tested on emulators and real hardware, plus their backend APIs.
Learn more ApplicationsDesktop & Thick Client Testing
Reverse-engineering local binaries for privilege escalation, DLL hijacking and logic flaws.
Learn more Network & CloudExternal Network Penetration Testing
Your internet-facing perimeter, attacked the way a real outsider would.
Learn more Network & CloudInternal Network & Active Directory Testing
Assume-breach testing from inside your network, with paths to domain compromise.
Learn more Network & CloudWireless Penetration Testing
On-site Wi-Fi testing: rogue access points, weak authentication and guest-network segmentation.
Learn more Network & CloudCloud Penetration Testing
AWS, Azure and GCP: IAM, misconfiguration and exploitation paths to your data.
Learn more ICS / OTICS / OT & SCADA Penetration Testing
Safety-first testing of PLCs, HMIs, RTUs and the IT/OT boundary — including control-room AI.
Learn more Red Team & HumanRed Team Engagements
Objective-based adversary emulation that tests detection and response — not just controls.
Learn more Red Team & HumanSocial Engineering & Phishing
Phishing, vishing and pretexting campaigns that measure the human layer.
Learn more Red Team & HumanPhysical Security Testing
Tailgating, badge cloning and lock bypass to test the defenses around your facilities.
Learn more Programs & CompliancePentesting as a Service (PTaaS)
Ongoing, on-demand testing that keeps pace with your releases.
Learn more Programs & ComplianceVulnerability Assessment
Broad, scanner-driven discovery validated by a human to cut the false positives.
Learn more Programs & ComplianceThreat Modeling
Map how an attacker would target your system before you build or ship it.
Learn more Programs & ComplianceCompliance Penetration Testing
SOC 2, PCI DSS, HIPAA, ISO 27001, NIST AI RMF and CMMC-aligned testing and reporting.
Learn moreDeal blocked by a security questionnaire or audit deadline?
Tell us the date. We reply within 24 hours with a scope that fits it — and an attestation letter your customer will accept.
Nothing matches that search. Tell us what you need tested — scoping it is our job.
Your AI is an insider. We test it like one.
LLM apps read your documents, call your APIs and act with your permissions. We test all ten OWASP LLM Top 10 (2025) risks by hand and map every finding to MITRE ATLAS. Select a risk to see how we attack it.
Prompt Injection
Inputs — typed or hidden in files, web pages and retrieved content — override the model's instructions.
We plant indirect injections in documents, emails and web content your AI reads, then chain them into tool calls.
Every test is scoped to you.
Price depends on what's in scope — applications, user roles, AI agents, hosts and on-site work. Web and AI testing have published starting prices, PTaaS runs as a subscription, and everything else gets a fixed proposal after a short scoping call.
Web App & API Penetration Test
Manual testing of a web application and its APIs — the test most SOC 2, insurance and customer security reviews ask for.
- Authenticated testing across user roles
- OWASP WSTG & API Top 10 coverage
- Auditor-ready report & attestation letter
- Free retest of all findings within 6 months
- Final price set by scope
AI & LLM Security Assessment
An LLM app, copilot or agent tested end to end — prompts, retrieval, tools and permissions.
- Prompt injection & jailbreak testing
- Data leakage & system prompt extraction
- Agent, tool & MCP abuse (if present)
- OWASP LLM Top 10 & MITRE ATLAS mapping
- Final price set by scope
Pentesting as a Service (PTaaS)
Ongoing, on-demand testing built into your development cycle — not a once-a-year snapshot.
- Continuous vulnerability discovery
- Real-time finding delivery
- Retests included during your term
- Quarterly reporting for SOC 2 evidence
- White-label option for MSPs
Everything else — fully scoped
External & internal network, Active Directory, cloud, mobile, desktop apps, ICS/OT, red team, wireless, physical, threat modeling and vulnerability assessments — or any combination.
- Free scoping call, reply within 24 hours
- Fixed scope, price and timeline
- Combine any of our 19 disciplines
- Compliance mapping on request
- Covered under NDA
Kill Chain Replay™
Scanners hand you a list. We hand you the path — every step an attacker would take, reproducible by your engineers and mapped to the frameworks your auditor knows.
Scope & threat model
We map assets, data flows and what an attacker would actually want — then agree rules of engagement in writing.
- Asset & data-flow inventory
- Threat-actor profile
- Rules of engagement
- Emergency contacts
Dereck Coleman
Founder & Principal Operator
Adversaries by training. Defenders by mission.
Ghost Ops isn't a scan-and-report shop. Every engagement is run personally by a named, credentialed operator — no juniors, no scan-with-a-logo, no handoffs.
Dereck spent 14 years in the U.S. Air Force learning that you can't defend what you've never attacked. He brings that same planning and rigor to the newest attack surfaces — AI and LLM systems, ICS/OT environments and full-scope offensive testing.
Evidence your auditor and your customers will accept.
Every report maps findings to the framework you're measured against — and is ready to upload to your compliance platform (Vanta, Drata, Secureframe and others).
| Framework | What it asks for | What you get from us |
|---|---|---|
| SOC 2 | CC4.1 / CC7.1 — monitoring and vulnerability identification | Annual pentest report + attestation letter |
| Cyber insurance | Proof of recent third-party testing at application or renewal | Executive summary underwriters can read |
| PCI DSS v4.0 | Req. 11.4 — internal, external and segmentation testing | Documented methodology + segmentation validation |
| HIPAA | §164.308(a)(8) — periodic technical evaluation | Findings tied to systems handling ePHI |
| ISO/IEC 27001:2022 | Annex A 8.8 — technical vulnerability management | Findings mapped to Annex A controls |
| NIST AI RMF | MEASURE 2.7 — AI security and resilience evaluated | AI red team report mapped to OWASP LLM Top 10 & MITRE ATLAS |
| CMMC Level 2 | NIST SP 800-171 assessment controls | Findings mapped to your SSP and POA&M |
Flip through a real sample report.
The report is the product. This is our 35-page web application assessment format — an illustrative engagement, not a real client.
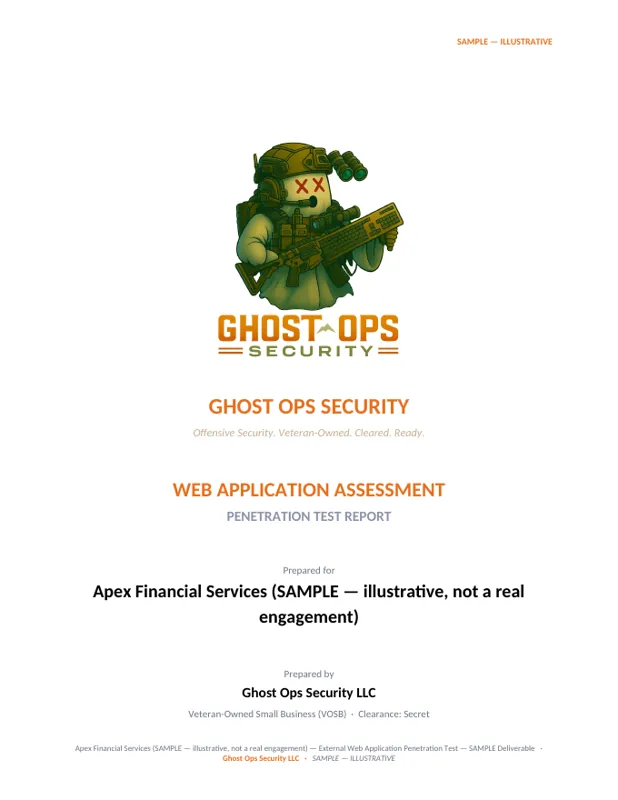
Cover
Branded deliverable with engagement details and classification.
- Executive summary & risk score
- 8 findings with CVSS, CWE, OWASP & ATT&CK mapping
- Reproduction steps, commands & evidence
- Kill Chain Replay™ attack path with detection gaps
- Remediation roadmap with SLAs
- Compliance mapping
AI red team sample report available on request — info@ghostops-security.com
Original research, not recycled headlines.
PHP2Shell: What Pentesters and Defenders Need to Know About CVE-2026-109618 and CVE-2026-109619
Your Model File Is Executable Code
Ghosts in the Machine: Your AI Is an Insider — and Attackers Know It
Wherever you are, we come to the target.
We test clients across the United States. Most work runs remotely; anything that needs boots on the ground, we travel for.
Remote testing
Web apps, APIs, mobile apps, cloud, external networks and AI/LLM systems — tested over the internet, no travel needed.
On-site testing
Physical security, wireless, on-site social engineering, internal networks and ICS/OT — we travel to your facilities anywhere in the U.S.
Internal testing without travel
Internal network and Active Directory tests can run remotely through a secure VPN or jump host you provide — same depth, lower cost.
What buyers ask before they hire us
What is penetration testing?
Penetration testing is an authorized, simulated attack on your systems by a security professional to find and safely exploit vulnerabilities before real attackers do. You receive a report showing what was reachable, how, and how to fix it.
How much does a penetration test cost?
It depends on scope — the number of applications, user roles, AI agents or hosts, and whether on-site work is needed. Web app and API tests start at $5,500 and AI/LLM assessments start at $7,500. Every engagement gets a fixed proposal before work begins, so there are no hourly surprises.
What is AI red teaming?
AI red teaming is adversarial testing of AI systems — LLM apps, agents and the tools they can use — to find ways an attacker can manipulate them, extract data or trigger unauthorized actions. We map findings to the OWASP LLM Top 10 and MITRE ATLAS.
Will your report satisfy our SOC 2 auditor?
Yes. Reports include methodology, scope, risk-rated findings, remediation guidance and an attestation letter, and map to the SOC 2 criteria auditors review. We also map to PCI DSS, HIPAA, ISO 27001, NIST AI RMF and CMMC on request.
What's the difference between a vulnerability scan and a penetration test?
A vulnerability scan is automated and lists known weaknesses. A penetration test is performed by a person who exploits and chains weaknesses to show real impact. SOC 2 and PCI DSS auditors generally expect a true penetration test.
How often should we get a penetration test?
At least once a year and after major changes — a new application, infrastructure migration or AI feature. Teams shipping weekly often move to continuous testing (PTaaS).
How long does a penetration test take?
A single web application or AI assessment typically takes about two weeks from kickoff to report. Larger or multi-discipline engagements are scheduled in your proposal.
Who actually performs the test?
Dereck Coleman, Ghost Ops' founder and principal operator, runs every engagement personally. Your test is never handed off to a junior or an automated scan.
Is the retest really free?
Yes. Every one-time engagement includes one free retest of all reported findings, any time within 6 months of the final report. Tell us when your fixes are in and we verify each one and issue an updated report and attestation letter.
Do you offer continuous testing (PTaaS)?
Yes. Pentesting as a Service gives you ongoing, on-demand testing integrated into your development cycle, with real-time findings, retests and quarterly reporting — on a subscription scoped to how often you ship.
Do you work with MSPs?
Yes. We provide white-label or co-branded testing for MSP clients with a referral program, so you can offer pentesting without building a team.
How do we get started?
Book a free 15-minute attack-surface review or a 30-minute scoping call on Calendly, email info@ghostops-security.com, or use the scoping form on our Contact page. We reply within 24 hours.
Do you work with companies outside your area?
Yes. We work with clients across the United States. Most testing runs remotely, and we travel for on-site work like physical security, wireless and ICS/OT — wherever your facilities are.